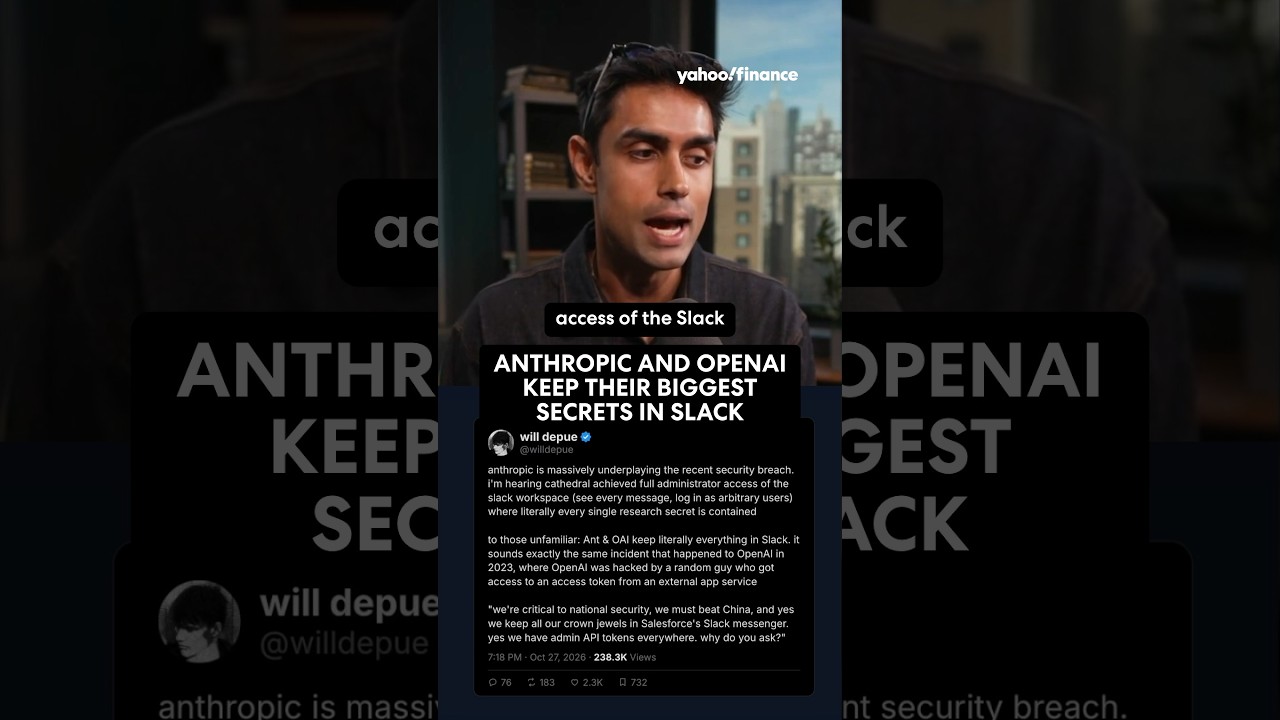
Cybersecurity startup Cathedral exploited a vulnerability in third-party software to gain access to Anthropic's internal systems, including Slack messages, sales data, HR records and IT infrastructure. Anthropic confirmed the breach but said it lasted several days and did not expose source code, model weights or user chat data. Will Depue, a former OpenAI researcher, suggests Anthropic may be understating the severity of the incident. The breach raises questions about whether AI labs developing safety-critical systems should face higher security standards than other technology companies.
This is an AI-written summary. The original reporting belongs to @YahooFinance. How we write these · Spot a mistake?